Cilium-Associate Exam Questions & Answers
Cilium Certified Associate (CCA) • Linux Foundation
100% money-back guarantee
Sample Cilium-Associate Questions
Practice with real exam-style questions, each with the verified correct answer and explanation.
Which question does Hubble provide the information to answer?
Hubble provides network and security flow observability derived from Cilium's datapath. Its flow records include source and destination workloads, namespaces, identities, ports, protocols, forwarding verdicts, and drop reasons. Hubble can therefore identify services or workloads whose connections were rejected by network policy. The Hubble CLI supports filtering by verdict, such as --verdict DROPPED, and official examples show events labeled Policy denied DROPPED. These capabilities directly answer the question posed in option D.
Option B, which is marked as correct in the supplied bank, is not supported by the stated functionality. Hubble may expose network-layer or supported application-layer metadata, including DNS and HTTP information when Layer 7 visibility is configured, but it is not a database query profiler and cannot determine which internal SQL statement ran longest merely from ordinary Hubble flows. Similarly, CPU utilization is a workload-resource metric normally obtained through Kubernetes metrics, Prometheus, or another monitoring system. Cilium BGP configuration is examined through Cilium configuration and BGP status commands rather than inferred from Hubble network flows.
The supplied answer key should therefore be corrected from B to D.
Official references
Inspecting Network Flows with the Hubble CLI; Hubble internals.
Study Guide topic: Network Observability.
This an Ingress configuration. What is the equivalent Gateway API configuration?
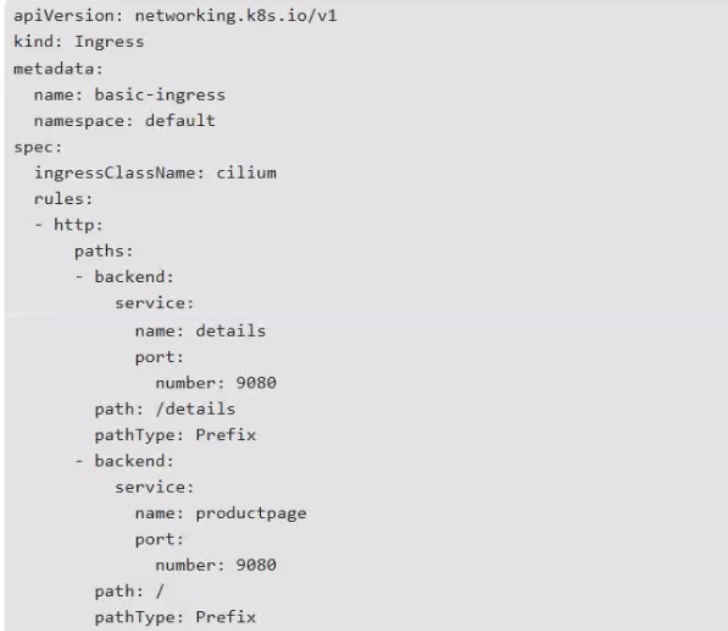
Question 19 source Ingress
A)
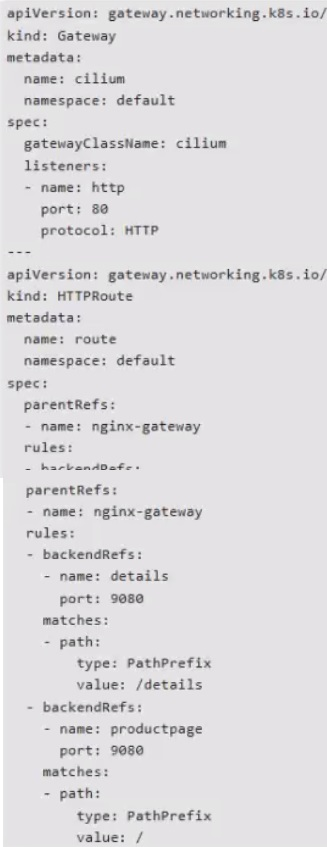
Question 19 option A
B)
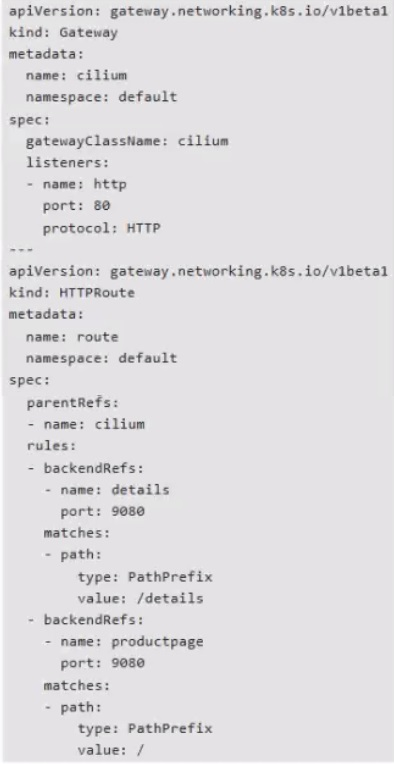
Question 19 option B
C)
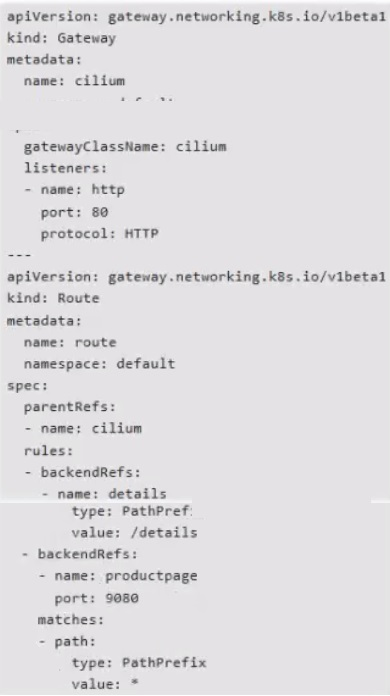
Question 19 option C
D)
Question 19 option D
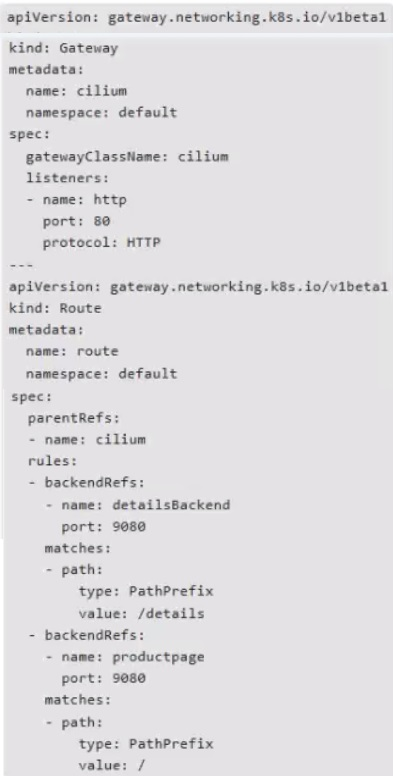
Option B correctly represents the Ingress as a Gateway and an attached HTTPRoute. The Gateway is named cilium, uses gatewayClassName: cilium, and exposes an HTTP listener on port 80. The HTTPRoute uses parentRefs with the same Gateway name, cilium, so the route attaches to the declared listener. Its two rules preserve the original routing behavior: /details with PathPrefix targets the details Service on port 9080, while / with PathPrefix targets productpage on port 9080.
Option A declares a Gateway named cilium but attaches its route to nginx-gateway. Because the parent reference does not identify the displayed Gateway, it is not equivalent. Options C and D use kind: Route; the correct resource kind for HTTP path routing is HTTPRoute. They also contain malformed or altered backend and matching fields. Option D changes the details backend name, while option C contains incorrect route structure and path content.
Cilium's official migration example uses the same conversion pattern: the Ingress class becomes the Gateway's class, paths move into HTTPRoute.rules, and the route identifies its Gateway through parentRefs.
The supplied key incorrectly identifies A. The verified answer is B.
Official references
HTTP Migration Example.
Study Guide topic: Service Mesh.
Which encapsulation protocols are supported when configuring Cilium in tunnel mode?
Cilium tunnel mode supports VXLAN and Geneve encapsulation. In this routing model, Cilium nodes form an overlay mesh, and traffic exchanged between nodes is carried inside UDP-encapsulated packets. VXLAN is the default tunnel protocol and normally uses UDP port 8472. Geneve is the alternative and normally uses UDP port 6081. Operators select the protocol through the tunnel-protocol configuration setting, whose documented values are vxlan and geneve.
Encapsulation reduces the requirements placed on the underlying network. The underlay only needs to provide IP connectivity between the Kubernetes nodes and permit the selected UDP tunnel port. It does not need to learn or route individual PodCIDRs. Cilium also uses the tunnel metadata to carry information such as the source security identity, avoiding an additional identity lookup on the receiving node.
MPLS, OTV, STT, and EVPN are not supported values for Cilium's tunnel-protocol setting. EVPN may be used in broader data-center network designs, and MPLS is a carrier-routing technology, but neither is a Cilium overlay encapsulation choice. Therefore, B is the only supported pair.
Official references
Cilium Routing; System Requirements.
Study Guide topic: Architecture.
If you are required to block ingress traffic from external IPs for all pods in your cluster, which of the following network policies would be the best fit?
A cluster-wide requirement is best implemented with CiliumClusterwideNetworkPolicy, whose correct resource spelling is CiliumClusterwideNetworkPolicy. Unlike a namespaced CiliumNetworkPolicy, this Cilium CRD is non-namespaced and can select endpoints across the entire cluster.
To deny external ingress for every Cilium-managed pod, a cluster-wide policy can use an empty endpointSelector and an ingressDeny rule selecting the world entity. Cilium defines world as network endpoints outside the cluster. An alternative allow-list construction can permit only the cluster entity, thereby excluding external sources, but an explicit deny rule usually communicates the requirement more directly.
A standard Kubernetes NetworkPolicy and a CiliumNetworkPolicy are namespaced, requiring repeated resources in every applicable namespace. CiliumGlobalPolicy is not a valid Cilium resource type. Although the option capitalizes ''Wide'' differently from the actual kind, D unmistakably identifies the intended cluster-scoped policy.
Official references
Cilium Deny Policies, Cilium Network Policy Types
Study Guide topic: Cluster-scoped policies, external traffic, and reserved entities.
Which Cilium command should you execute to gather network-related troubleshooting information from your Kubernetes cluster?
The intended answer is D, but the option contains a source-bank typographical error. The valid command is cilium sysdump, not cilium sysduwp. Read literally, none of the four displayed commands exactly answers the question.
The Cilium CLI's sysdump operation gathers cluster-wide troubleshooting material, including Cilium configuration and endpoint state, agent and operator logs, Kubernetes workload information, routing and interface details, kernel messages, service state, policies, and selected eBPF-map output. This consolidated archive is the preferred diagnostic package when investigating Kubernetes networking or preparing a support report.
cilium status --verbose provides expanded health and deployment status, but it does not collect the comprehensive diagnostic archive requested. debuginfo is associated with the in-agent debug client---currently documented as cilium-dbg debuginfo---and produces useful local-agent API information; in Kubernetes environments it is already included as part of the system dump. cilium bugtool is not the current cluster-wide Cilium CLI command requested here.
For an exam-ready correction, option D should read cilium sysdump.
Official references
Cilium Troubleshooting and Sysdump
Study Guide topic: Cilium CLI troubleshooting, system dumps, and diagnostic collection.
Get access to all 60 verified questions with detailed answers.
Unlock All Cilium-Associate Questions